
Rebalancing the Risk Function
Why banks must move beyond compliance routines and restore Risk Management as a strategic, forward-looking discipline.
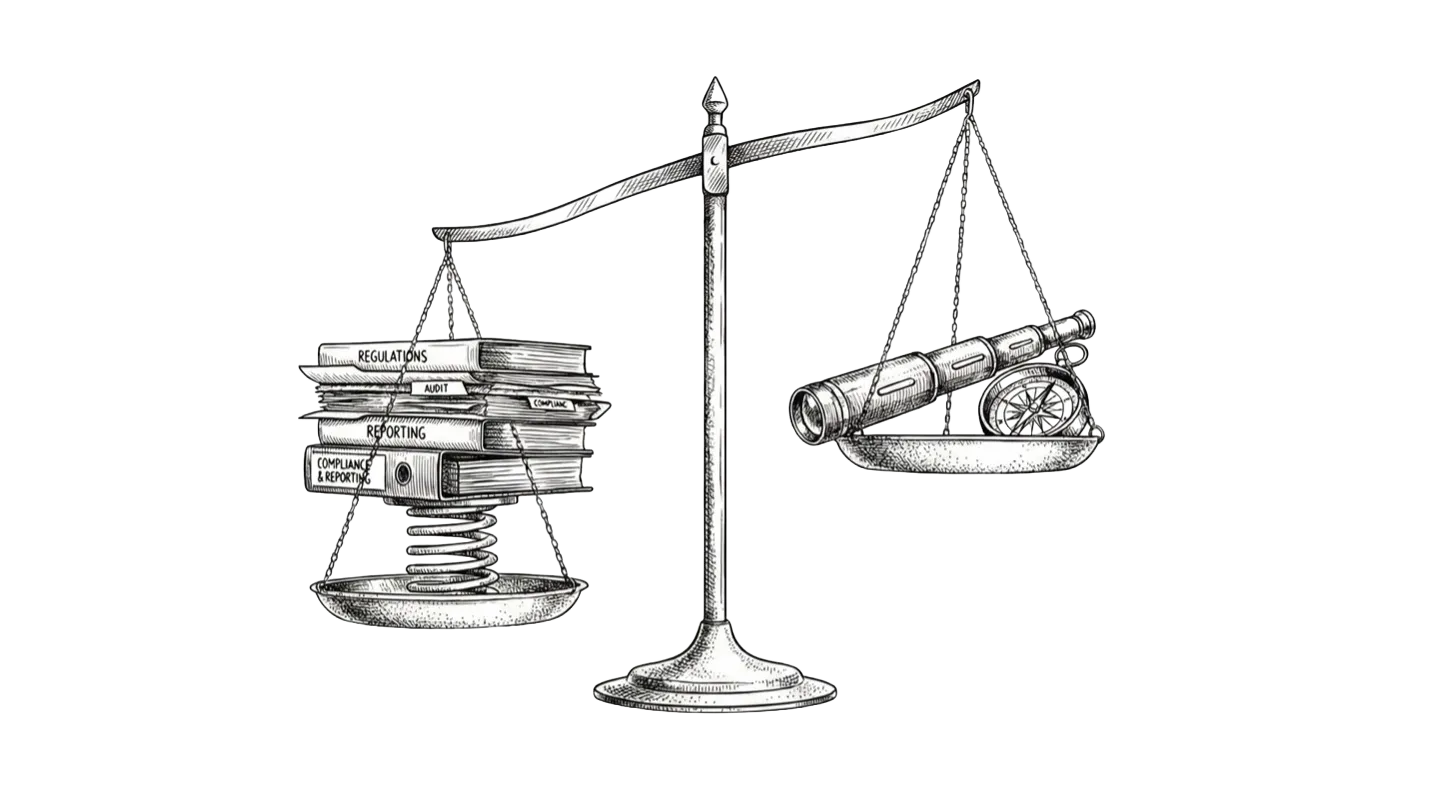
This post is a summary of the white paper Rebalancing the Risk Function. The full white paper goes deeper into the examples, drivers, and practical implications for CROs and boards. The complete document can be provided on request.
Why does this matters now
Banks have entered a period of sustained uncertainty marked by geopolitical fragmentation, tighter financial conditions and rapid technological change, while many risk functions are still optimised for demonstrating compliance rather than managing the unexpected. The question is no longer whether controls are “strong enough”, but rather is Risk Management still equipped to see what comes next.
Walk into any banking risk conference and the agenda feels familiar, Basel III/IV, stress testing, model validation, reporting, operational resilience. These topics matter and they have made banks safer. But their dominance also reveals a shift in the profession’s centre of gravity. Over the last decade, the industry has become very good at proving control and less focused on managing uncertainty.
This is not an argument against regulations. To the contrary, capital, liquidity and governance standards have risen materially since the global financial crisis. Supervisory scrutiny has increased, and much of it has been constructive and necessary. In the EU in particular, the supervisory cycle and the intensity of interaction, SREP expectations, stress testing regimes, operational resilience requirements, and expanded model governance, have pushed risk functions to become highly structured, highly evidenced, and highly repeatable.
The unintended consequence is that, in many banks, risk has come to operate primarily as an assurance function, optimised to pass inspections, close findings and populate templates. That is not the same as a strategic risk capability that helps senior management to anticipate change, understand second-order effects, and shape decisions before the environment forces them.
Risk Management and Risk Control are not opposites
A recurring source of confusion is treating Risk Management and Risk Control as interchangeable. They are not. They serve different purposes.
Risk Management is strategic and forward-looking. It is about choices under uncertainty:
- How much risk is the institution willing to accept in pursuit of its strategy?
- Where are fragilities and concentrations building that are not yet visible in today’s metrics?
- How might risks interact across silos and how would the bank behave if key assumptions break?
- Which risks should be deliberately run, and which should be avoided, reduced or priced differently?
Risk Control is operational and assurance-focused. It translates risk appetite into day-to-day guardrails, such as limits, controls, monitoring and escalation, and provides confidence those guardrails are operating as intended.
Risk compliance is narrower still: the reporting, documentation and audit trail that demonstrates adherence to regulatory and internal requirements.
These elements should reinforce one another. In practice, they have drifted out of balance. Risk Control and compliance have expanded rapidly, absorbing time, talent and budget that might otherwise have been devoted to anticipatory risk thinking. This has resulted in strong controls, but with diminished foresight.
This distinction also clarifies accountability. Risk is owned in the first line (business, operations and technology), where most controls actually operate. The second line sets frameworks, challenges and synthesises. The third line provides independent assurance. A bank is only “in control” if the first line has the incentives, data and decision discipline to act, not only if the second line can evidence compliance.
Why control keeps winning
This imbalance did not emerge by accident. It is the product of rational responses to the environment banks operate in.
Regulatory tightening raised the baseline
Post-2008 reforms increased capital, leverage and liquidity requirements; strengthened stress-testing expectations and expanded supervisory focus into areas such as model risk and operational resilience. In the EU, SSM/SREP has embedded regular assessment cycles that reward predictable execution via high-quality evidence, clean submissions, clear remediation plans, and reliable timetables.
Reporting demands grew materially
Even where regulators are working on harmonisation, banks still face multiple authorities, different definitions, and increasing granularity. Operational resilience requirements added new registers, testing expectations and third-party oversight. The risk function has become, by necessity, a production line for credible documentation.
Accountability changed behaviour
Individual accountability regimes increase the personal liabilities for senior management. When careers and reputations are at stake it is understandable that senior management’s attention tilts toward what is demonstrable and auditable.
Automation amplified the dynamic
To cope with volume, most banks have invested in regulatory data warehouses, workflow tooling, model inventories and tooling for reporting. This has improved consistency and auditability. But automation has also reinforced a template-driven approach in many organisations where success is defined by throughput, completeness and accuracy of reporting taxonomies, rather than by how well the bank can explore uncertainty beyond the rulebook.
Each of these forces are defensible in isolation. Together, they create a system that systematically rewards Risk Control behaviours, because they are measurable, schedulable, auditable and closely tied to external outcomes.
What tends not to evolve at the same pace is the harder work: enterprise synthesis, scenario-driven debate, and judgement under uncertainty. Activities that do not fit neatly into templates, yet matter when the environment changes fast.
The structural constraint: data, IT and organisation
A major reason this pattern persists is structural as a result of data, technology and organisational fragmentation.
Many banks still operate with:
- multiple core systems with inconsistent identifiers;
- separate data stacks for finance, risk, regulatory reporting and front office analytics; and
- a heavy reliance on manual reconciliations and end-user computing to stitch together what is needed for reporting and control.
Supervisors address data quality issues by increasing validation rules and audit trails, prompting banks to add more controls and reinforcing a cycle where manual checks consume resources and delay system improvements. As a result, maintaining control becomes the primary focus.
Enterprise risk teams often struggle in this environment, as policy-driven approaches can turn them into coordinators without clear data ownership or analytical depth across various risk types. This leads to many dashboards but no effective enterprise-level view of how uncertainties might generate losses.
The practical outcome is familiar. Strategic analytics and forward-looking work is repeatedly deferred, because the cost of keeping the compliance factory running is immediate and non-negotiable.
Rebalancing without weakening control
Rebalancing the risk function does not mean weakening controls or lowering standards. It means restoring Risk Management as a strategic discipline alongside a strong control framework.
How to make those shifts in a way that is realistic, given ongoing compliance backlogs, cost pressure and accountability constraints, is the focus of the white paper. It addresses how uncertainty can be framed, how risk insights can be synthesised for decision-makers, how risk data and IT can be treated as strategic infrastructure, and how governance time and incentives can be allocated without simply “doing more”.
A deliberately blunt conclusion
Risk controls and their supporting compliance measures are essential, but alone they are inadequate in an increasingly complex, uncertain, and volatile environment. As regulations often trail emerging risks, organisational resilience relies not only on adhering to supervisory standards but also on reinvigorating the strategic and proactive foundation of Risk Management, namely cultivating the ability to anticipate shifts, analyse interdependencies, and make informed decisions proactively rather than reactively.